Weaponized AI: Inside Modern Cyber Attacks
Sat, 7 Nov 2026 · 3:00 PM EAT · 1 hour
A free moderated panel on how AI is reshaping cyber attacks, seen from the offensive, business, and SOC perspectives. Live Q&A included.
Hands-on ethical hacking, penetration testing, and cyber defense training. Built for Africa's next generation of security professionals.
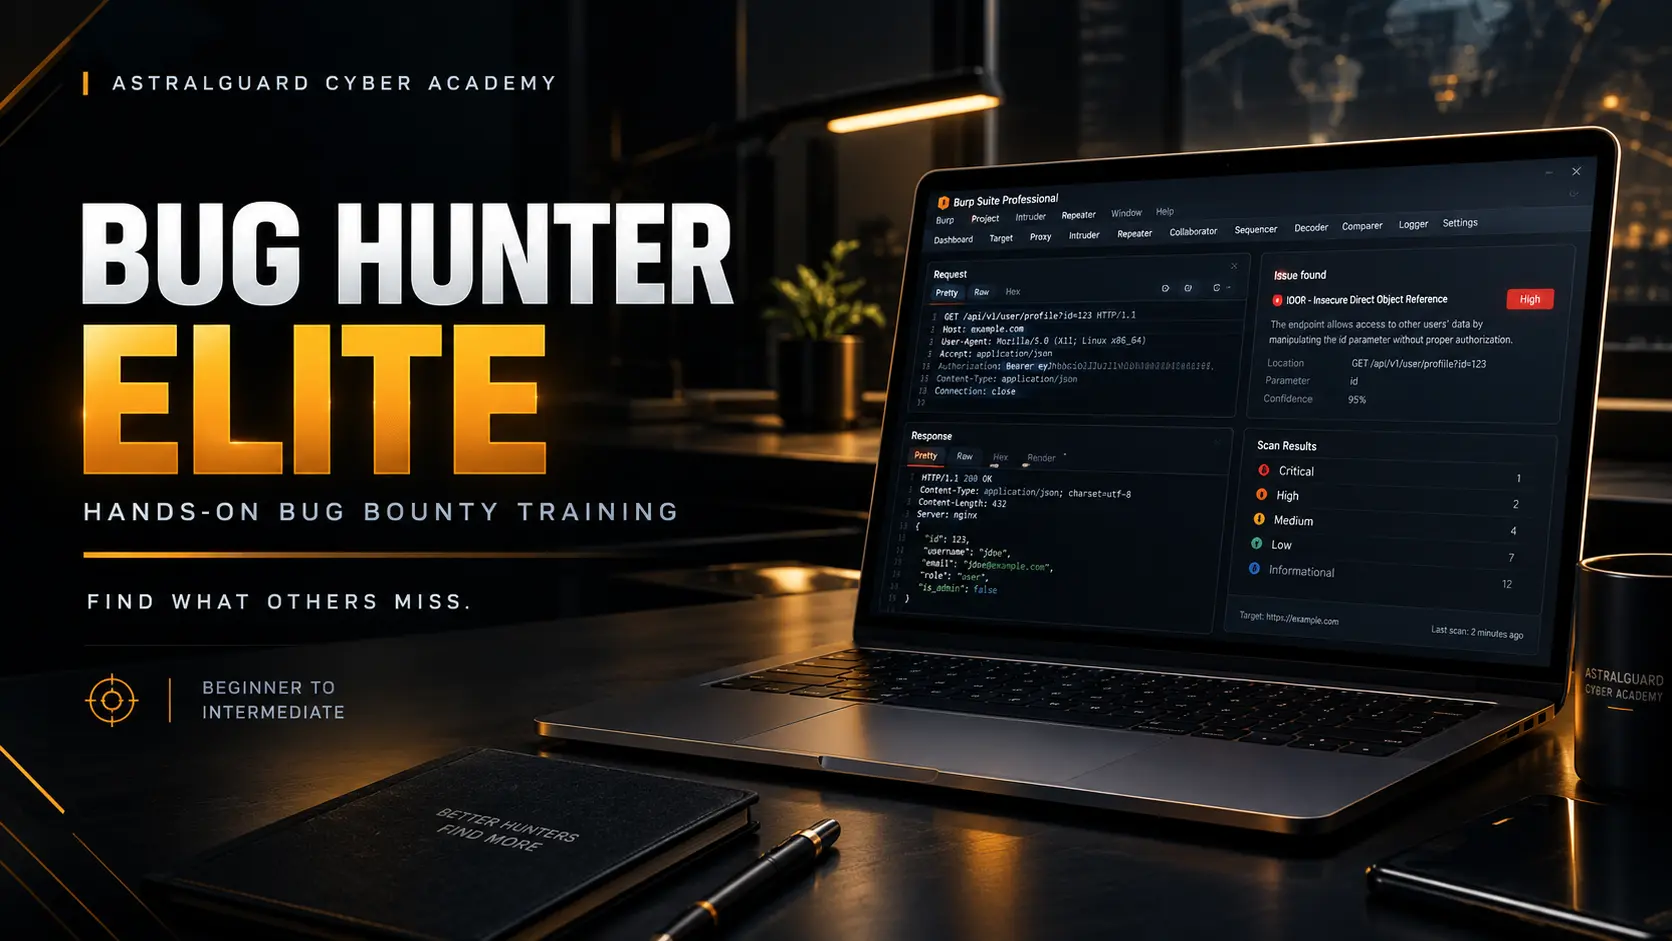
Enrollment in ProgressLearn How to Hunt the Bugs Other Hunters Skip Most beginners lose months to the same four mistakes. Hunting on oversaturated programs. Reporting bugs that were found hours earlier. Breaking scope and program rules. Joining programs that never pay or scam programs. Experienced hunters avoid all four. This course shows you how, live, with an active bug bounty hunter beside you. You will choose a real program, hunt rare vulnerability classes on it, and submit your first report before the course ends. Built for complete beginners and intermediates. Why Most Hunters Stay Unpaid Valid, clear, in-scope reports get paid. Skill alone does not. Most hunters fail for reasons that have little to do with how much they know: They pick programs with too much competition They spend weeks on common bugs that are almost always duplicates They submit reports that triage teams cannot reproduce They make rule mistakes that get them banned They put time into programs that pay late or not at all Bug bounty rewards the hunter who picks the right target, finds what others miss, and reports it clearly. This course gives you that method. Tools You'll Master You will use these on live targets, not demo labs. Burp Suite Turbo Intruder Param Miner ffuf Subfinder httpx Nuclei You will learn which tool fits which target, when to skip automation, and how to build a workflow of your own. What You'll Be Able To Do By the end of this course, you will confidently: 1. Choose low-competition programs that match your strengths 2. Spot oversaturated and scam programs before you waste time on them 3. Read scope and rules and know exactly what is allowed 4. Avoid the mistakes that get hunters banned 5. Set up your platform account and payout method 6. Hunt rare vulnerability classes that most hunters skip 7. Write clear reports that triage teams can reproduce 8. Submit a real report to a live program You will leave with a repeatable hunting method and a 30-day plan to keep going. Learning Mode This is live from start to finish. In the hunting weeks, every week follows the same loop: Learn: the instructor teaches one rare bug class. Hunt alone: you test it on a live program during the week. Hunt together: the instructor reviews your attempt and hunts with you live, so you see your own mistakes. You also get: Live sessions with an active bug bounty hunter. Hunting on real programs. Your first report, reviewed and submitted. A 30-day plan to keep hunting after the course. Cohort Discord support. Where This Skill Takes You Independent Bug Bounty Hunter. Application Security (AppSec) Engineer. Product Security Engineer. Penetration Tester. Red Team Operator. Security Researcher Who This Course Is For Complete beginners who want a clear path into bug bounty Intermediate hunters tired of duplicates and N/A reports Penetration testers moving into bounty hunting Developers who want to find flaws the way attackers do Security students building real-world experience No course can promise a payout. This one gives you the method, live practice, and a submitted report.
Registration closes 11/13/2026
Handbook
Handbook
Sat, 7 Nov 2026 · 3:00 PM EAT · 1 hour
A free moderated panel on how AI is reshaping cyber attacks, seen from the offensive, business, and SOC perspectives. Live Q&A included.
Our next selective intake. Interns spend 62 days working on hands-on security tasks with practicing experts, fully online.
Real mentors check in and slow down when material gets hard, not a self-paced content dump.
24/7 hands-on lab access across every program, built for practice, not passive watching.
We run cohorts with real instructor availability, quality over volume, always with real attention.
“I've really enjoyed my experience studying at Astralguard. The courses have been informative and relevant, and the instructors have been helpful in explaining complex topics. The hands-on labs and approach have been great for building practical skills. I've learned a lot and would recommend Astralguard to anyone interested in cybersecurity.”

AI SecurityOld, obscure systems were once safe because nobody bothered to attack them. AI has removed that protection. Here is what changed and what defenders should do about it.
Read article
Cybersecurity EducationKnowing the theory and being able to apply it are two different things. Here is why that gap exists in cybersecurity education, what it costs students, and how to start closing it yourself.
Read articleReal mentors, real labs, real cohorts. See what's open right now.
Browse Courses